One investigative perspective
Connected evidence.
Clearer questions.
About CRIMEX
Building a connected
investigative picture
Our mission
Keep complaints, evidence and observations in one traceable case record, with decisions in human hands.
Our approach
Make sources visible. Separate demonstration data from evidence. State what has—and has not—been checked.
Our purpose
Context for a
connected world
A suspicious endpoint, an unfamiliar account or an altered file is a starting point—not a conclusion.
CRIMEX brings supplied case information together so analysts can inspect the record, understand its limits and decide what comes next.
More about CRIMEXConnected capabilities
A complete view
of your
investigation
Cybercrime investigation
Complaints, supplied entities and analyst observations in one case record.
Explore moduleDigital forensics
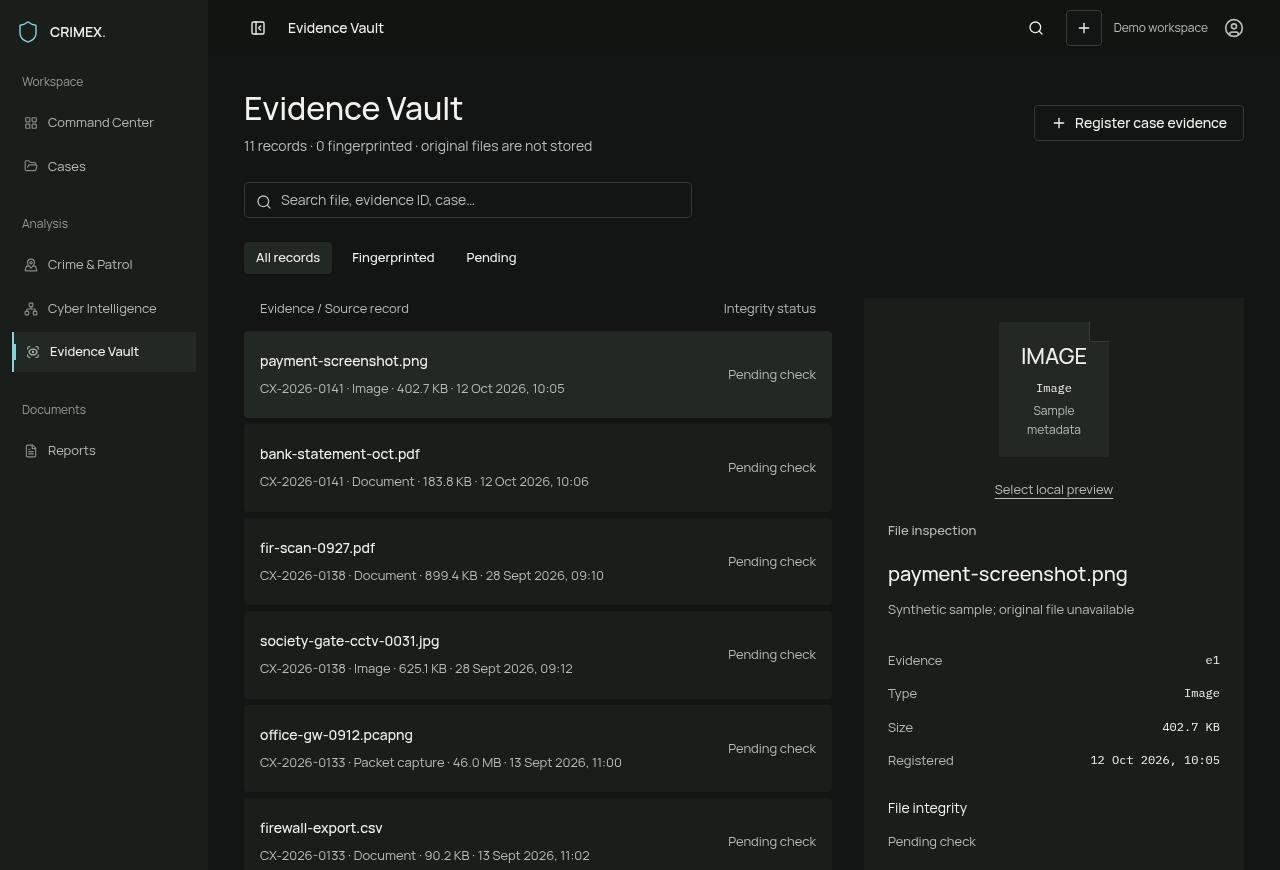
Local file previews and integrity checks. Media forensic engines remain unconfigured.
Explore moduleNetwork & PCAP
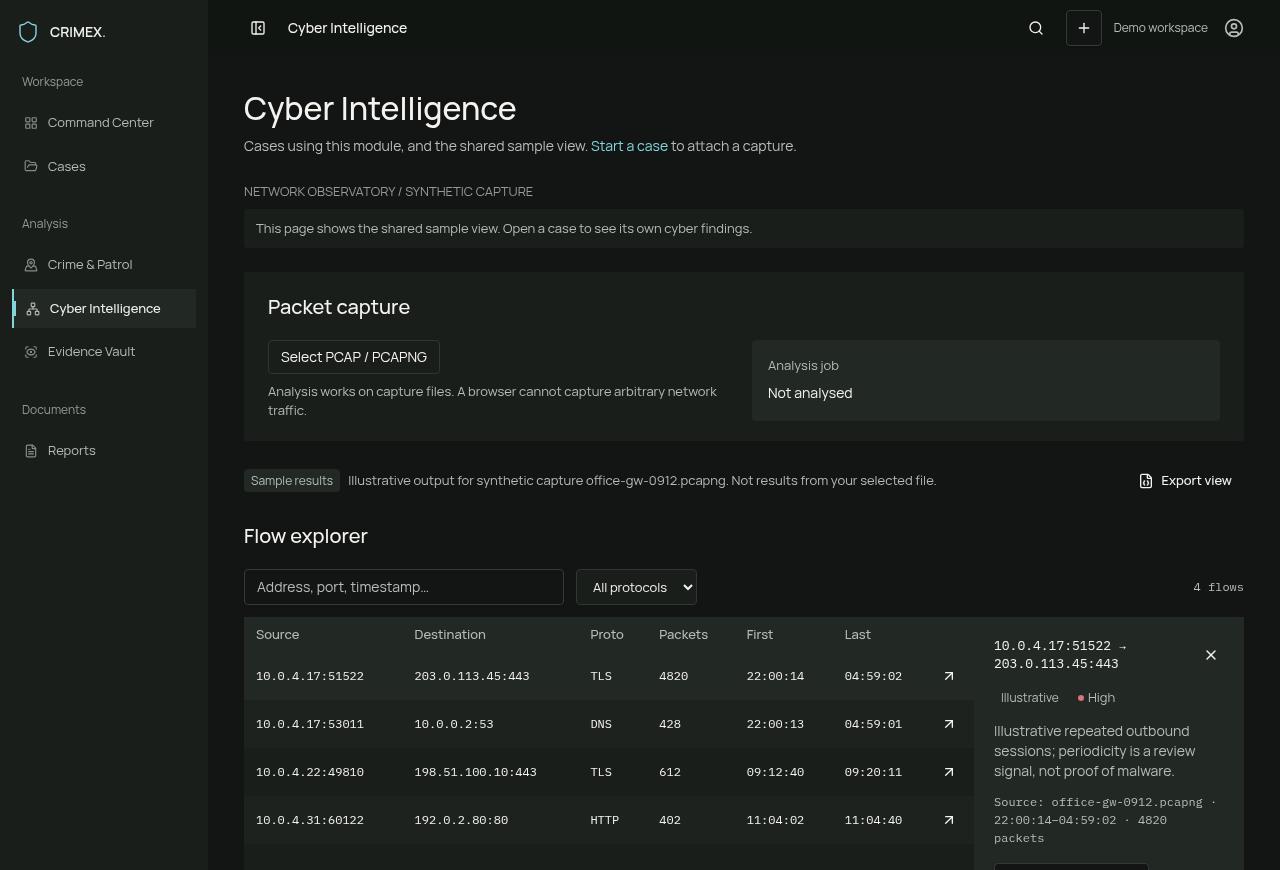
Inspect synthetic packet flows and source context. Uploaded packet parsing is not connected.
Explore moduleEvidence integrity
Calculate SHA-256, compare a trusted reference and retain the check history.
Explore moduleThe investigation workflow
Follow the signal.
Keep the source.
Demonstration scenarios
A clue. Its context.
The next question.
Fictional example / 01
Suspected account compromise
Compare supplied login observations with the synthetic network example. No compromise is confirmed.
- Source types
- Authentication log · Network indicator
- Review focus
- Authentication logs
Fictional example / 02
Payment fraud complaint
Bring the complaint, supporting records and analyst notes into one reviewable case.
- Source types
- Transaction record · Supplied identifier
- Review focus
- Financial records
Fictional example / 03
Cyber-physical incident
Inspect supplied geographic context alongside evidence references, without inventing associations.
- Source types
- Incident location · Digital evidence
- Review focus
- Geographic context
Investigative methodology
Confidence starts with
knowing the limits.
01 / 03 — Evidence principles
Source before conclusion
Every observation should retain its evidence reference. An association is not a finding until an analyst reviews it.
The CRIMEX platform
One case.
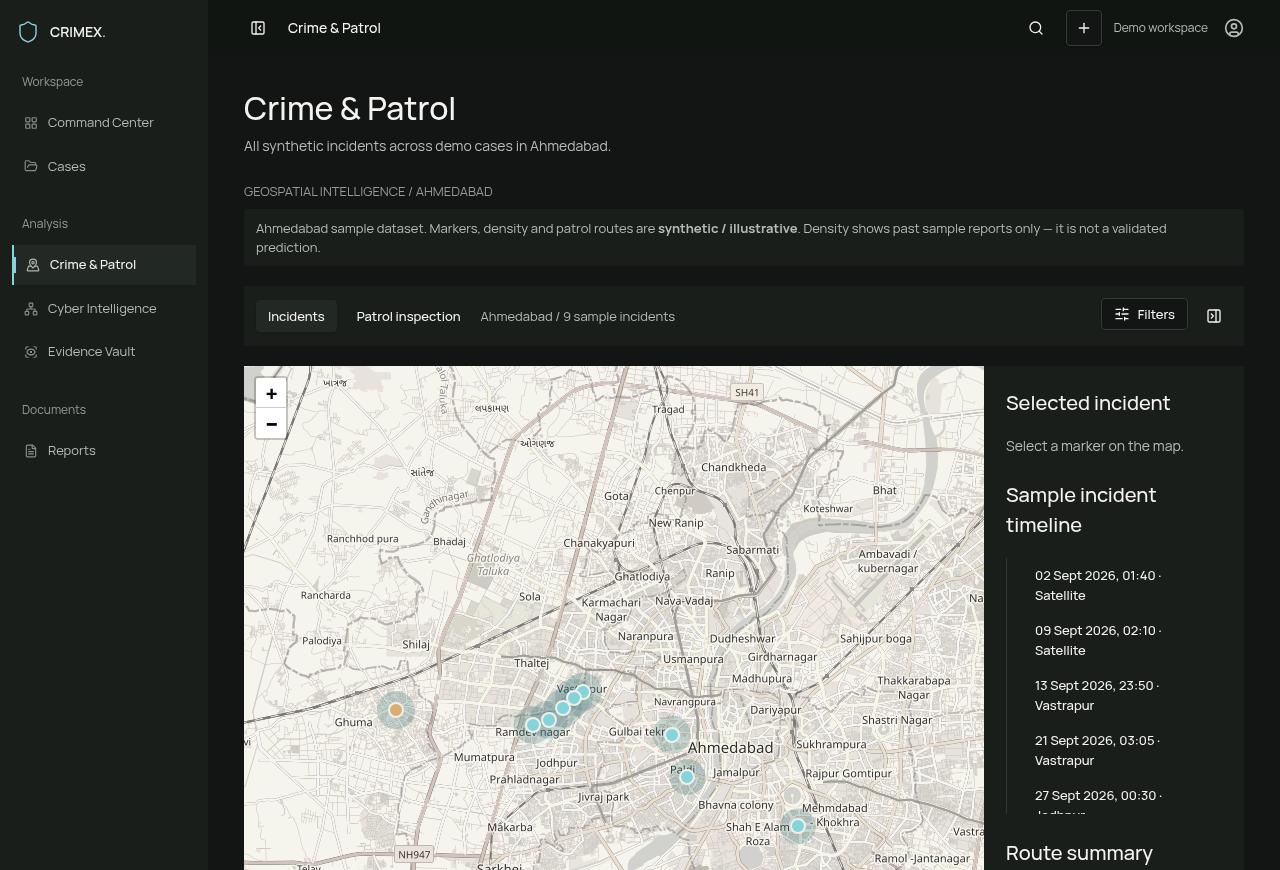
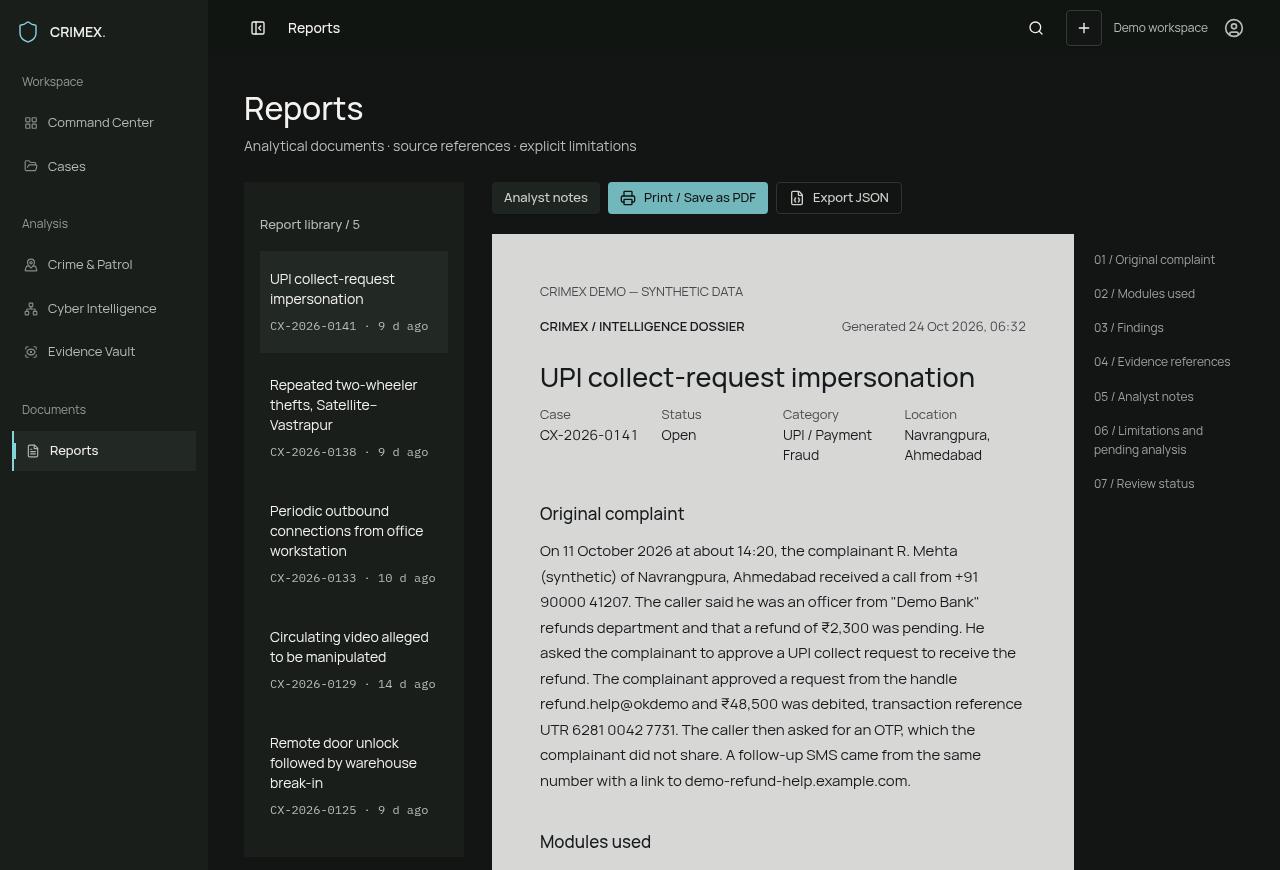
Six connected workspaces.
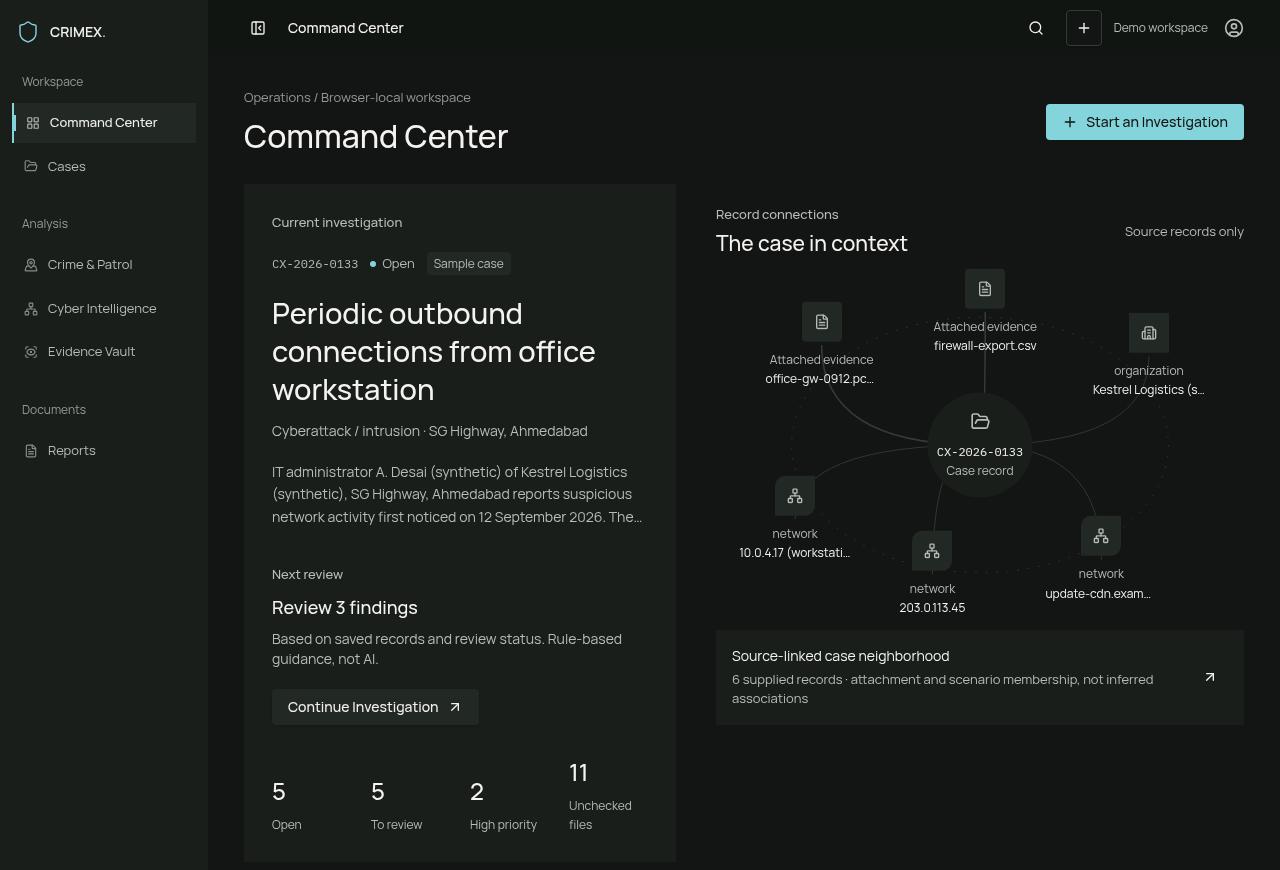
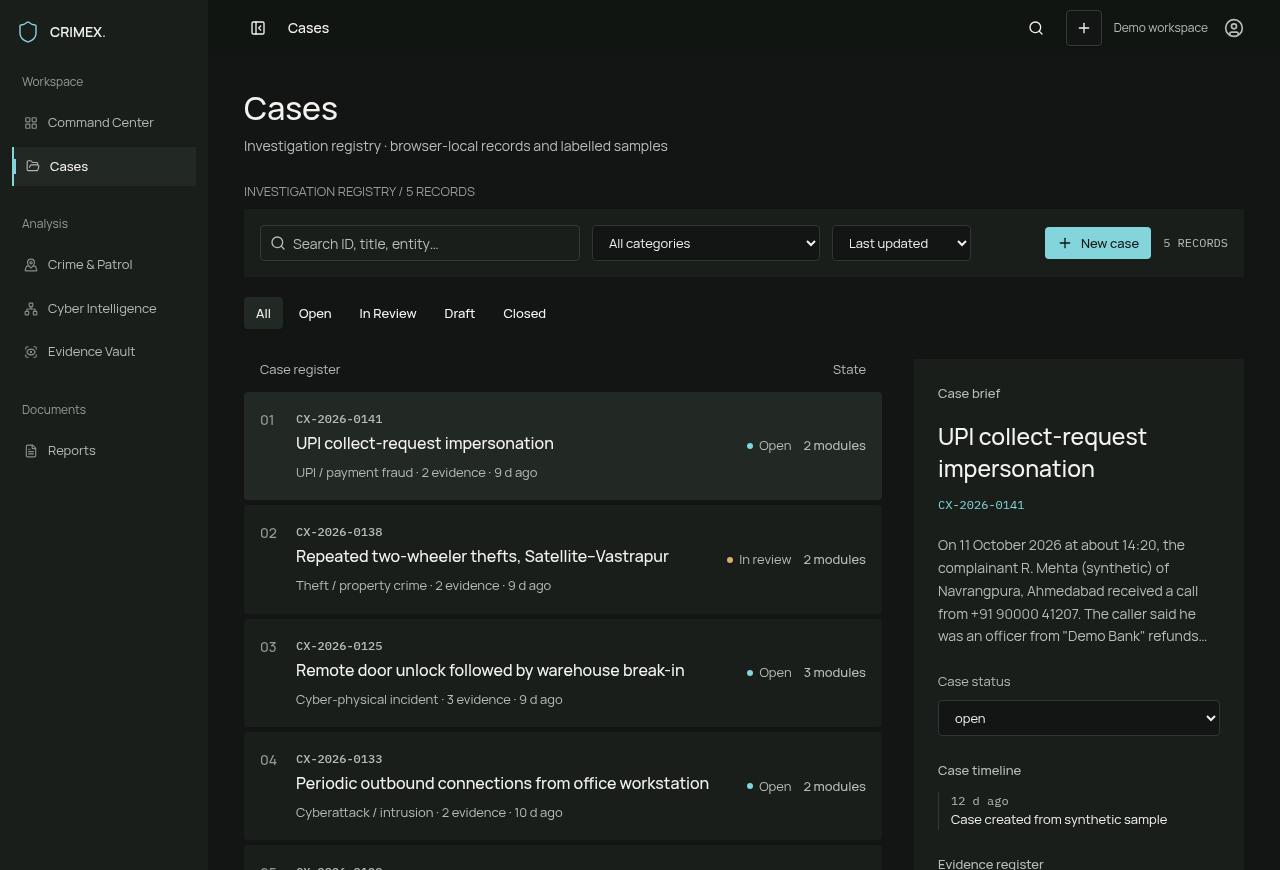
Actual CRIMEX screens.
Browser-local demonstration.
Your next investigation
Start with a case.
See where it leads.
A complaint, its sources and your findings.
One traceable investigation record.
Technical resources